The Legal Problem
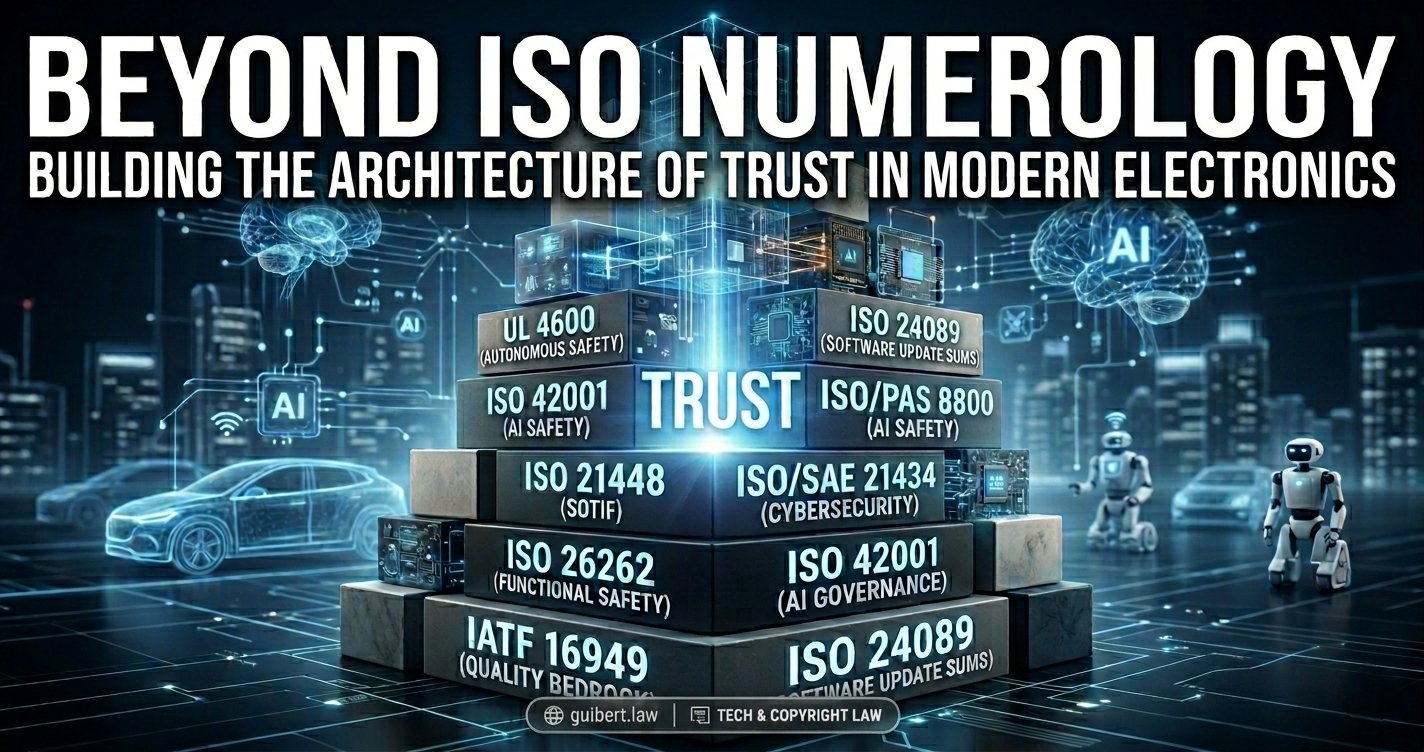
ISO 21448:2022 Safety of the Intended Functionality (SOTIF) addresses a category of hazard that ISO 26262 does not: hazards arising not from hardware faults or systematic failures, but from performance limitations and triggering conditions in the intended functionality itself. For AI-enabled perception, decision, and control systems, SOTIF is the relevant safety standard, and its legal significance is substantial.
The SOTIF distinction matters in litigation because it changes the liability theory. A hardware fault failure is a question of whether the design met the ISO 26262 standard of care. A performance-limitation failure raises the question of whether the developer adequately identified, characterized, and mitigated known triggering conditions, a question that goes to negligent design and failure to warn, not just manufacturing defect.
What guibert.law Delivers
- SOTIF validation documentation review for legal defensibility
- Performance limitation liability analysis for AI-enabled system architectures
- ISO/PAS 8800 AI safety for road vehicles: obligations analysis and contract provisions
- Disclosure strategy for known AI system limitations
- Product liability defense preparation for AI-involved incidents
guibert.law Insight
The triggering condition database required by ISO 21448 is a double-edged artifact. From an engineering perspective, it documents the systematic effort to identify and mitigate known failure modes. From a litigation perspective, it is a record of what the developer knew, and when they knew it. Legal review of triggering condition documentation is essential before any public disclosure or regulatory filing.
← Back to Embedded Systems Functional Safety